Summary: Cloud DDoS providers filter attack traffic before it reaches your network. Key evaluation criteria include mitigation capacity, network layer coverage, time to mitigation and SLA, deployment model, and incident support. Radware is best for hybrid deployments, Akamai Prolexic is best for large-scale scrubbing, Cloudflare is best for broad web coverage, and AWS Shield Advanced is best for AWS-hosted workloads.
How to Choose a Trusted Cloud DDoS Mitigation Provider
Choosing a trusted cloud DDoS protection provider requires matching your infrastructure type (web-only vs. all-network traffic), deployment model, and network scale against top-tier vendor capabilities.
These providers typically combine large network capacity with automated detection and traffic filtering. Depending on the service, protection can cover network and transport layer attacks, such as UDP floods and SYN floods, as well as application layer attacks targeting HTTP endpoints, APIs, and other services.
Key evaluation criteria for trusted providers:
- Mitigation capacity and scrubbing footprint: total filtering capacity and how many locations it is spread across
- Attack coverage across network and application layers: which layers, protocols, and asset types are protected
- Time to mitigation and SLA commitments: how fast filtering starts and what the provider contractually guarantees
- Deployment model and infrastructure fit: always-on, on-demand, or hybrid, and how traffic is routed to the provider
- Visibility, reporting, and incident support: dashboards, attack data, and access to the provider's response team
Solutions compared in this guide:
Dedicated cloud DDoS mitigation providers:
- Radware Cloud DDoS Protection Services: Behavioral L3–L7 defense with flexible deployment
- Akamai Prolexic: Dedicated global scrubbing with zero-second mitigation SLA
- Imperva DDoS Protection: Fast L3/4 mitigation across websites, networks, and IPs
- NETSCOUT Arbor Cloud: Hybrid carrier-grade mitigation with cloud signaling
Edge platform and cloud infrastructure providers:
- Cloudflare DDoS Protection: Massive edge capacity for web, app, and network defense
- Fastly DDoS Protection: Edge-based adaptive mitigation for applications and APIs
- AWS Shield Advanced: Native AWS DDoS protection with managed incident support
- Azure DDoS Protection: Always-on Azure mitigation with adaptive traffic tuning
Why Choosing the Right DDoS Protection Provider Matters
Choosing the right DDoS protection provider is important because an attack can affect revenue, customer trust, and application performance within minutes. A strong provider should detect attacks quickly, filter traffic accurately, and keep critical services available without slowing legitimate users.
- Impact of downtime on revenue and customer trust: DDoS-related outages can stop transactions, disrupt customer interactions, and increase support or recovery costs. Repeated downtime can also push users toward competitors.
- Risks of slow or ineffective mitigation: Delayed detection or traffic diversion can allow attacks to overwhelm networks and applications. Poor filtering may either let malicious traffic through or block legitimate users.
- Importance of protecting application availability and performance: Protection should preserve uptime, latency, and reliability. Effective providers combine network-level and application-aware controls to defend against both volumetric and targeted attacks.
How to Choose a Cloud DDoS Protection Provider
Each criterion below covers a different part of the decision. Work through all five before shortlisting, since a provider can rate well on capacity and still be a poor fit for how your traffic is routed.
Mitigation Capacity and Scrubbing Footprint
Capacity is the total volume of attack traffic a provider can filter at once, usually stated in terabits per second. Footprint is how that capacity is distributed across scrubbing centers or points of presence. A large aggregate number matters less if the capacity sits far from where your attack traffic originates, because traffic has to be hauled across the internet before it is cleaned. Providers also differ in whether capacity is dedicated to DDoS scrubbing or shared with content delivery and other services.
Evaluation criteria:
- What is the stated mitigation capacity, and is it dedicated to DDoS or shared with other platform traffic?
- How many scrubbing centers or points of presence exist, and in which regions?
- Is traffic mitigated close to its source through anycast routing, or hauled to a central location?
- Can the provider absorb several large attacks at the same time?
Attack Coverage Across Network and Application Layers
Volumetric floods at layers 3 and 4 and application-layer floods at layer 7 need different detection methods. Network-layer filtering handles UDP floods, SYN floods, and reflection attacks. Application-layer filtering has to separate HTTP request floods from legitimate spikes, which usually requires behavioral analysis rather than static thresholds. Coverage also varies by asset type: some services protect web properties only, while others extend to DNS, individual IPs, and non-HTTP protocols.
Evaluation criteria:
- Are layer 3, layer 4, and layer 7 attacks all covered, or only some of them?
- Does coverage extend to DNS, APIs, individual IPs, and non-HTTP protocols?
- How are encrypted and TLS-based application floods handled?
- Is layer 7 detection behavioral, or does it rely on static rules and rate limits?
Time to Mitigation and SLA Commitments
The gap between attack start and filtering start determines how much downtime you absorb. Always-on services filter continuously, so mitigation begins immediately. On-demand services need traffic diverted first, which adds delay. SLAs turn these claims into commitments, and the specific wording matters: some cover time to mitigate, others cover platform availability or network uptime.
Evaluation criteria:
- What is the stated time to mitigation, and does it differ by attack layer?
- Is there a contractual SLA covering time to mitigate, and what does it exclude?
- Are separate SLAs offered for platform availability and network connectivity?
- Does mitigation start automatically, or does it require manual activation?
Deployment Model and Infrastructure Fit
How traffic reaches the provider constrains which services you can realistically use. Web properties can often be onboarded with a DNS change. Whole networks usually need BGP advertisement, GRE tunnels, or a cross connect, which requires a routable address block. Cloud-native services protect resources inside a single provider's environment and do not extend to assets hosted elsewhere. Hybrid models pair on-premises hardware with cloud scrubbing for volumetric overflow.
Evaluation criteria:
- Does the service support always-on, on-demand, and hybrid deployment?
- What routing method is required, and do you meet the prerequisites such as a /24 IPv4 block or BGP capability?
- Does protection cover multi-cloud and on-premises assets, or only one environment?
- How does the service integrate with your existing WAF, CDN, and SIEM?
Visibility, Reporting, and Incident Support
During an incident, teams need to see what is being blocked, why, and whether legitimate users are affected. After an incident, they need attack data for post-mortems and compliance reporting. Support models vary from self-service dashboards to fully managed services where the provider's operations centre runs mitigation on your behalf. Data retention limits and log export options are worth checking early, since they are difficult to work around later.
Evaluation criteria:
- What attack telemetry is available in real time, and how long is historical data retained?
- Can logs be exported to a SIEM, and how much configuration does that take?
- Is a 24/7 response team included, and is it advisory or fully managed?
- Does the provider offer runbooks, readiness drills, or post-incident analysis?
Common Cloud DDoS Protection Providers and How They Meet the Criteria
The table summarises how each provider measures up against the five criteria. Each is examined in detail in the sections that follow.
| Category |
Provider |
How It Meets the Criteria |
| Dedicated cloud DDoS mitigation providers |
Radware Cloud DDoS Protection Services |
30 Tbps across 25 scrubbing centers with behavioral detection at layers 3, 4, and 7, always-on, on-demand, and hybrid deployment, and an SLA covering detection, mitigation, and uptime. Managed by the Emergency Response Team. |
| Dedicated cloud DDoS mitigation providers |
Akamai Prolexic |
20+ Tbps of dedicated defense across 32 anycast scrubbing centers, with a zero-second mitigation SLA, 100% platform availability SLA, and in-cloud, on-premises, or hybrid deployment backed by a 24/7 SOCC. |
| Dedicated cloud DDoS mitigation providers |
Imperva DDoS Protection |
13 Tbps of scrubbing capacity covering websites, networks, DNS, and individual IPs, with a 3-second mitigation SLA for layers 3 and 4 and ISP-agnostic routing options. |
| Dedicated cloud DDoS mitigation providers |
NETSCOUT Arbor Cloud |
33 Tbps across 16 scrubbing centers reached via BGP or DNS, with mitigation initiation inside 60 seconds and hybrid operation through cloud signaling from on-premises Arbor Edge Defense. |
| Edge platform and cloud infrastructure providers |
Cloudflare DDoS Protection |
500 Tbps of network capacity covering websites, TCP/UDP applications through Spectrum, and networks through Magic Transit, with 24/7 support and an Under Attack hotline. |
| Edge platform and cloud infrastructure providers |
Fastly DDoS Protection |
578 Tbps of connected network capacity with adaptive rule generation at the edge, mitigation in seconds without tuning, and billing based on legitimate traffic only. |
| Edge platform and cloud infrastructure providers |
AWS Shield Advanced |
Inline mitigation across layers 3, 4, and 7 for AWS resources, with traffic baselining, Shield Response Team access during incidents, and cost protection for attack-driven usage. |
| Edge platform and cloud infrastructure providers |
Azure DDoS Protection |
Always-on monitoring and automatic mitigation for Azure virtual networks, with adaptive tuning against policy thresholds and a 15-minute rapid response team SLA. |
Notable Cloud DDoS Protection Providers
How we selected these providers: We shortlisted cloud DDoS protection services based on mitigation capacity, coverage across network and application layers, speed of mitigation and SLA commitments, deployment flexibility, and the visibility and incident support they provide.
Dedicated Cloud DDoS Mitigation Providers
1. Radware Cloud DDoS Protection Services
Best for: Hybrid estates needing always-on, on-demand or hybrid protection
Strengths: Behavioral detection, 25 scrubbing centers, 30 Tbps, managed ERT
Things to consider: Reporting retention and dashboard layout have fixed limits
Radware Cloud DDoS Protection Services filters DDoS traffic through a network of 25 fully connected scrubbing centers carrying 30 Tbps of mitigation capacity. Detection uses behavioral algorithms that build a baseline of normal traffic and generate signatures automatically when patterns deviate, which allows the service to act on attack types it has not seen before.
The service runs in three deployment modes. Always-on continuously routes traffic through Radware. On-demand diverts traffic only when a volumetric attack is detected, using link utilization thresholds, flow statistics, or manual triggers. Hybrid pairs an on-premises device with the cloud service, sharing baselines and attack footprints between the two in real time so that diversion does not create a protection gap.
Key features include:
- Behavioral detection and automatic signature creation: Traffic is analysed against learned baselines rather than fixed rules, and signatures are generated in real time to stop both infrastructure-layer and application-layer attacks.
- Three deployment models: Always-on, on-demand, and hybrid options cover different network topologies, including organisations that cannot deploy an on-premises mitigation device.
- Global scrubbing network: 25 fully connected scrubbing centers with 30 Tbps of capacity mitigate attacks closer to their point of origin.
- Service level agreement: The SLA covers detection time, mitigation time, and uptime commitments.
- Emergency Response Team as a managed service: Radware's ERT provides a single point of contact and manages attack events proactively, so customer involvement during an incident is minimal.
- Cloud Web DDoS Protection: An add-on covering application-layer DDoS attacks, including Web DDoS Tsunami attacks, that works with or without sharing TLS certificates.
- Consolidated asset view: Current and historical attack data is analysed from a single asset view rather than across separate consoles.
- Expansion options: Firewall as a Service, Threat Intelligence Service, Network Analytics, and AI SOC Xpert extend the service beyond DDoS filtering.
| Criterion |
Solution Fit |
Key Considerations |
| Mitigation capacity and scrubbing footprint |
30 Tbps across 25 fully connected scrubbing centers, with mitigation applied close to the attack source. |
Regional scrubbing center proximity affects latency, so confirm coverage for your primary traffic regions. |
| Attack coverage across network and application layers |
Behavioral detection covers infrastructure-layer and application-layer attacks; Cloud Web DDoS Protection adds layer 7 coverage with or without certificate sharing. |
Full application-layer and encrypted attack coverage comes through the Web DDoS add-on rather than the base service. |
| Time to mitigation and SLA commitments |
Hybrid mode starts mitigation on-premises in real time; the SLA covers detection, mitigation, and uptime. |
Time to protection depends on the deployment mode chosen, with on-demand slower than always-on by design. |
| Deployment model and infrastructure fit |
Always-on, on-demand, and hybrid modes support most network topologies, with diversion options based on link utilisation, flow statistics, or manual control. |
Reviewers note the initial setup and onboarding can take time and often involves Radware's team. |
| Visibility, reporting, and incident support |
Asset view consolidates current and historical attack data; the Emergency Response Team manages events as a fully managed service. |
Reviewers point to a fixed retention window for dashboard data and limited dashboard customisation. |
2. Akamai Prolexic
Best for: Large enterprises and providers needing dedicated scrubbing
Strengths: 32 scrubbing centers, zero-second SLA, 24/7 SOCC of 225+ staff
Things to consider: Premium pricing and much of the tuning sits with Akamai SOCC
Akamai Prolexic routes incoming traffic through Akamai infrastructure, inspects it, applies proactive or custom mitigation controls, and forwards only clean traffic to the origin. It runs across 32 anycast scrubbing centers with 20+ Tbps of dedicated DDoS defense capacity, backed by more than 1 Pbps of total Akamai network capacity.
Deployment covers in-cloud, on-premises through Corero, and hybrid combinations of the two. Connectivity options include Routed GRE, which requires an advertisable /24 IPv4 or /48 IPv6 block and BGP capability, and IP Protect for organisations with fragmented address space or cloud hosting. Prolexic over Akamai Direct Connect provides a private interconnection between the customer origin and Akamai with 10 G and 100 G port support.
Key features include:
- Anycast scrubbing at scale: 32 global scrubbing centers carry 20+ Tbps of dedicated DDoS defense, and anycast routing mitigates attack traffic closest to its source while applying collective platform capacity to the largest attacks.
- Zero-second mitigation SLA: Proactive mitigation controls stop more than 98% of attacks instantly, with a 100% platform availability SLA alongside the mitigation commitment.
- Flexible deployment: The service runs in-cloud, on-premises through Corero, or as a hybrid where on-premises scrubbing handles routine traffic and cloud capacity absorbs sustained large attacks.
- Always-on or on-demand operation: Always-on routes all inbound traffic through Prolexic; on-demand routes traffic only during an attack, with a facilitated route-on service available.
- Prolexic Network Cloud Firewall: A stateless cloud firewall at the network edge where you define geographic and IP-based ACLs, or have Prolexic suggest them, with API-driven integration into other security systems.
- Managed SOCC service: More than 225 frontline responders across six locations provide pre-attack, during-attack, and post-attack review and analysis, plus custom runbooks and operational readiness drills.
- Multi-protocol mitigation controls: Dynamic mitigation controls scale capacity to handle attacks across IPv4 and IPv6 traffic flows.
| Criterion |
Solution Fit |
Key Considerations |
| Mitigation capacity and scrubbing footprint |
20+ Tbps of dedicated defense across 32 anycast scrubbing centers, supported by 1+ Pbps of total network capacity. |
Capacity is sized for large enterprises and providers, which is reflected in pricing that reviewers describe as high. |
| Attack coverage across network and application layers |
Covers network and application layer attacks across IPv4 and IPv6, with the Network Cloud Firewall extending control beyond DDoS. |
Reviewers have raised false positives as a concern, requiring accuracy checks during onboarding. |
| Time to mitigation and SLA commitments |
Zero-second mitigation SLA with proactive controls stopping more than 98% of attacks instantly, plus a 100% platform availability SLA. |
Routing decisions and much of the tuning are handled by Akamai's SOCC, giving customers less direct control. |
| Deployment model and infrastructure fit |
In-cloud, on-premises via Corero, or hybrid, with Routed GRE, IP Protect, and Direct Connect options. |
Routed GRE requires a /24 IPv4 or /48 IPv6 block and BGP capability, so smaller estates need the IP Protect path. |
| Visibility, reporting, and incident support |
24/7/365 SOCC with 225+ responders, custom runbooks, readiness drills, and post-mitigation analysis. |
Reviewers describe logging as minimal given traffic volumes, and interface usability as an area for improvement. |
3. Imperva DDoS Protection
Best for: Websites, networks, DNS and individual IPs on one platform
Strengths: 13 Tbps scrubbing, 3-second L3/4 SLA, ISP-agnostic routing
Things to consider: Defaults and SIEM logging need review before production use
Imperva DDoS Protection operates as three services covering different asset types. DDoS Protection for Websites routes HTTP and HTTPS traffic through a secure proxy via a DNS change, masking the origin IP and filtering attack traffic alongside the cloud WAF. DDoS Protection for Networks shields whole infrastructures. DDoS Protection for Individual IPs handles non-HTTP assets and assets that regulation prevents a cloud WAF from inspecting.
All three draw on 13 Tbps of global scrubbing capacity. Anycast routing and real-time capacity management allocate resources across points of presence, and the service is ISP-agnostic, so it works with any provider without compatibility work.
Key features include:
- Three-second mitigation SLA for layers 3 and 4: Volumetric and protocol attacks are mitigated within a guaranteed three seconds, with network-layer attacks typically mitigated inside one second.
- Coverage across websites, networks, DNS, and individual IPs: Layer 3 and 4 attacks such as UDP floods, SYN floods, and DNS amplification are covered alongside layer 7 attacks such as HTTP GET and POST floods and SlowLoris.
- Multiple network connectivity options: Networks can be onboarded through GRE tunnels, cross connects, or virtual cross connects such as Equinix Fabric Cloud Exchange, in always-on or on-demand mode with flow-based monitoring and automatic or manual switchover.
- Machine learning thresholds for layer 7: Traffic patterns are analysed to set thresholds automatically, using heuristic, behavioural, and contextual analysis plus crowdsourced data, with only 0.01% of visitors seeing a CAPTCHA challenge.
- Anycast routing with real-time capacity management: Traffic is routed across efficient paths and monitored at every point of presence, with 95% of the world experiencing sub-50 millisecond latency.
- Self-service onboarding and automated operation: Settings are configured through a self-service portal, after which mitigation runs without manual intervention, including in on-demand mode.
- SIEM integration: DDoS events can be correlated with other security data through leading SIEM platforms.
| Criterion |
Solution Fit |
Key Considerations |
| Mitigation capacity and scrubbing footprint |
13 Tbps of global scrubbing capacity with anycast routing and real-time capacity management across points of presence. |
Capacity is lower than several other providers in this list, which matters for the very largest volumetric attacks. |
| Attack coverage across network and application layers |
Layer 3, 4, and 7 coverage across websites, networks, DNS, and individual IPs, including non-HTTP assets. |
Reviewers report that default settings can allow protection to be bypassed unless reviewed before production deployment. |
| Time to mitigation and SLA commitments |
Guaranteed three-second SLA for layer 3 and 4 attacks, with network mitigation typically inside one second. |
The three-second guarantee applies to layers 3 and 4; layer 7 timing is described as consistently fast but without the same commitment. |
| Deployment model and infrastructure fit |
DNS change for websites, GRE tunnels or cross connects for networks, IP Protection for individual assets, all ISP-agnostic. |
Reviewers describe configuration as not always straightforward and note occasional slow performance across modules. |
| Visibility, reporting, and incident support |
Self-service portal for configuration and management, real-time insights, SIEM integration, and an emergency DDoS mitigation team. |
Reviewers report that audit logging to SIEM has been challenging to configure. |
4. NETSCOUT Arbor Cloud

Best for: Carriers and enterprises pairing on-prem defense with cloud
Strengths: 33 Tbps across 16 centers, cloud signaling, ASERT intel
Things to consider: Deployment and tuning expect skilled network teams
NETSCOUT Arbor Cloud routes inbound traffic through 16 global scrubbing centers in Asia, Europe, and the Americas carrying more than 33 Tbps of mitigation capacity. Traffic reaches the service via BGP or DNS, and only clean traffic is returned to internet access links and servers.
The service targets three attack categories: high-volume attacks against bandwidth, low and slow attacks against applications and infrastructure, and simultaneous multi-vector attacks. It can run as a standalone cloud-only service invoked on demand, or combined with on-premises Arbor Edge Defense in a hybrid configuration linked by an automated cloud signal.
Key features include:
- Global scrubbing capacity: 16 worldwide scrubbing centers provide more than 33 Tbps of network mitigation capacity for large-scale volumetric attacks.
- Automated detection and diversion: Stateless packet-processing technology and cloud-based IP flow analysis detect attacks and route them to Arbor Cloud scrubbing centers automatically.
- Sub-minute mitigation initiation: Mitigation starts within 60 seconds of detection, triggered by cloud signaling from Arbor Edge Defense, by flow detection, or as part of an always-on configuration.
- Cloud-only or hybrid deployment: The service runs standalone on demand, or in combination with on-premises Arbor Edge Defense, which handles state-exhaustion and application attacks against firewalls, IPS devices, and business-critical applications.
- ATLAS and ASERT threat intelligence: Global threat intelligence from ATLAS and the ASERT research team feeds the service, drawing on automated malware analysis pipelines, sinkholes, scanners, honeypots, and open-source intelligence.
- Incident management with real-time feedback: Arbor Cloud DDoS specialists provide real-time feedback through a ticketing system, backed by a 24x7 security operations centre.
- Arbor Cloud WAF: An always-on web application firewall covering OWASP Top 10 risks with virtual patching and bot management.
| Criterion |
Solution Fit |
Key Considerations |
| Mitigation capacity and scrubbing footprint |
More than 33 Tbps across 16 scrubbing centers in Asia, Europe, and the Americas. |
Sixteen centers is a smaller footprint than some competitors, so regional proximity is worth confirming. |
| Attack coverage across network and application layers |
Covers volumetric, low and slow, and multi-vector attacks, with the Arbor Cloud WAF adding OWASP Top 10 and bot coverage. |
Full application-layer coverage depends on adding the WAF or pairing with on-premises Arbor Edge Defense. |
| Time to mitigation and SLA commitments |
Mitigation initiation within 60 seconds of detection via cloud signaling, flow detection, or always-on operation. |
The sub-minute commitment is slower than the near-instant claims made by several other providers. |
| Deployment model and infrastructure fit |
Cloud-only on demand, or hybrid with on-premises Arbor Edge Defense linked by automated cloud signal; traffic routed via BGP or DNS. |
Reviewers describe deployment and day-to-day tuning as complex and dependent on skilled network teams. |
| Visibility, reporting, and incident support |
24x7 ASERT-backed SOC, real-time feedback through a ticketing system, and ATLAS threat intelligence. |
Reviewers cite cost as a recurring concern and note reporting timestamps not always aligning with event times. |
Edge Platform and Cloud Infrastructure Providers
5. Cloudflare DDoS Protection
Best for: Web properties, APIs and networks needing quick onboarding
Strengths: 500 Tbps capacity, L3/4 to L7 coverage, Under Attack hotline
Things to consider: Advanced controls sit in higher tiers and take time to learn
Cloudflare DDoS Protection absorbs attack traffic across a global network with 500 Tbps of capacity, which the company states is 23 times larger than the biggest DDoS attack recorded. Protection runs on the same infrastructure that carries Cloudflare's other services, so websites, applications, and networks are covered from one platform.
Coverage is split across three products. Standard DDoS protection handles websites and web applications. Spectrum extends protection to applications built on any protocol, including custom protocols running on servers, containers, or virtual machines. Magic Transit covers networks, data centers, and infrastructure against layer 3 and layer 4 attacks.
Key features include:
- Network capacity for volumetric absorption: 500 Tbps of network capacity absorbs large-scale attacks without degrading performance for legitimate traffic.
- Website and web application protection: Sites and applications stay reachable during large attacks, with mitigation applied across the global network.
- TCP and UDP application security through Spectrum: Applications using any protocol, including custom ones, are protected across boxes, containers, and virtual machines.
- Network and data center defense through Magic Transit: Networks, data centers, and infrastructure are protected against layer 3 and layer 4 attacks.
- 24/7 support and Under Attack hotline: Email and phone support run continuously, with a dedicated Under Attack hotline for immediate assistance.
- Straightforward onboarding: Turning on DDoS protection is a configuration step rather than an infrastructure project.
| Criterion |
Solution Fit |
Key Considerations |
| Mitigation capacity and scrubbing footprint |
500 Tbps of global network capacity, shared with Cloudflare's delivery and security services rather than dedicated to scrubbing. |
Capacity is platform-wide rather than DDoS-dedicated, which is a different model from scrubbing-center providers. |
| Attack coverage across network and application layers |
Websites and web applications, TCP and UDP applications via Spectrum, and networks via Magic Transit. |
Full coverage requires combining products, so scope and cost depend on which assets you need protected. |
| Time to mitigation and SLA commitments |
Mitigation is applied inline across the global network so services stay online during attacks. |
The product page does not state a specific time-to-mitigate SLA. |
| Deployment model and infrastructure fit |
Onboarding is designed to be simple, with protection running on the same infrastructure as Cloudflare's other services. |
Reviewers describe complex setup and a steep learning curve for advanced configuration. |
| Visibility, reporting, and incident support |
24/7 email and phone support plus an Under Attack hotline for immediate response. |
Reviewers note that many useful features require higher-priced plans, and that the interface is complex to navigate. |
6. Fastly DDoS Protection
Best for: Application and API teams wanting one-switch edge mitigation
Strengths: 578 Tbps network, adaptive rule building, no attack billing
Things to consider: Aimed at app and API traffic, with paid support tiers
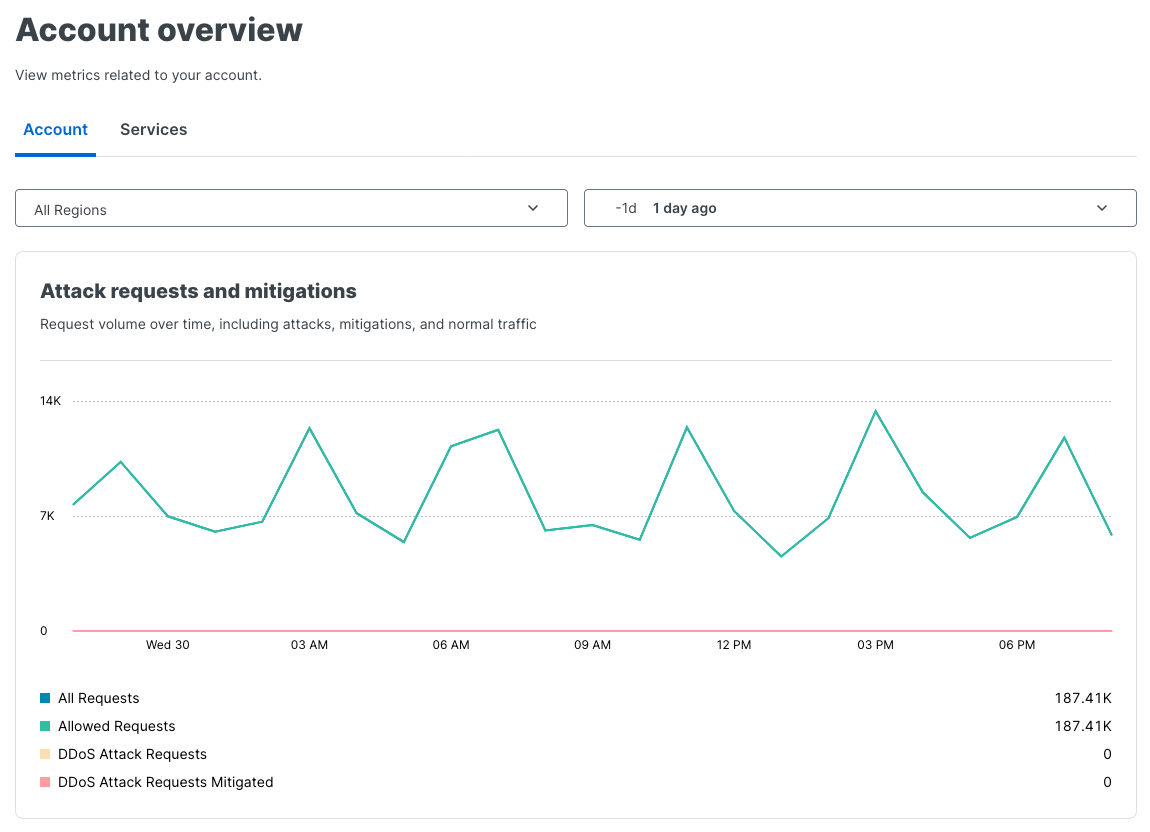
Fastly DDoS Protection mitigates attacks at the network edge rather than diverting traffic to a scrubbing center. The service runs on a global network offering 578 Tbps of capacity as of 31 March 2026, absorbing network-layer attacks and dropping non-HTTP and non-HTTPS traffic automatically for anyone on the platform.
Detection is handled by the Adaptive Threat Engine, which builds tailored rules for each attack rather than applying static rulesets. When unexpected volumetric traffic appears, the engine validates whether it is legitimate and, if not, scans a list of characteristics to isolate and mitigate the attack even when the source rotates IP addresses.
Key features include:
- Adaptive rule generation: The Adaptive Threat Engine builds rules per attack and updates signatures in near real time, so rotating attacks can be blocked without manual tuning.
- Edge-based mitigation: Detection and mitigation logic sits at the network edge alongside delivery logic, rather than in a centralised scrubbing center.
- Network capacity for volumetric attacks: 578 Tbps of connected global capacity absorbs large network-layer attacks, with irrelevant non-HTTP and non-HTTPS traffic dropped automatically.
- Near real-time mitigation: Attacks are blocked in seconds, including multiple synchronised attacks at once, without tuning.
- Rule-level visibility: Every rule generated to fight an attack is visible, so teams can verify that legitimate traffic is not being blocked.
- Billing based on legitimate traffic: Customers are billed on legitimate traffic only, so volumetric attacks do not incur delivery and egress fees.
- Platform-agnostic deployment: Protection can be deployed on-premises, in the cloud, or in hybrid environments through a DNS change or by integrating the edge cloud platform, with no hardware installation.
| Criterion |
Solution Fit |
Key Considerations |
| Mitigation capacity and scrubbing footprint |
578 Tbps of connected global network capacity absorbing attacks at the edge. |
Capacity is shared platform capacity rather than dedicated scrubbing, and published figures are dated snapshots. |
| Attack coverage across network and application layers |
Application and API DDoS mitigation with automatic dropping of non-HTTP and non-HTTPS traffic at layers 3 and 4. |
The service is oriented to application and API traffic rather than full network infrastructure protection. |
| Time to mitigation and SLA commitments |
Attacks are blocked in seconds with mitigation applied at the edge on detection. |
The product page describes speed but does not state a contractual time-to-mitigate SLA. |
| Deployment model and infrastructure fit |
Enabled with a single switch, deployable via DNS change or platform integration, with no hardware and no tuning required. |
Reviewers describe integration and WAF configuration as difficult in places, and documentation availability as a gap. |
| Visibility, reporting, and incident support |
Visibility into every rule crafted for an attack, so mitigation decisions can be verified. |
Reviewers report slow support response times and high licensing costs relative to alternatives. |
Source: Fastly
7. AWS Shield Advanced
Best for: Workloads hosted on AWS behind CloudFront, ALB and Route 53
Strengths: Inline L3 to L7 mitigation, Shield Response Team, cost cover
Things to consider: Key features are Advanced-tier only and scoped to AWS
AWS Shield Advanced provides managed DDoS protection for resources running on AWS, applying automatic inline mitigation across layers 3, 4, and 7. Detection draws on AWS global threat intelligence, and mitigation runs without manual intervention.
The service also baselines normal traffic for each application, so anomalies such as HTTP floods and DNS query floods are detected against the application's own behaviour rather than a generic threshold. AWS Shield also includes network security director, currently in preview, which analyses AWS resources and configurations to surface misconfigured or overlooked assets.
Key features include:
- Automatic inline mitigation across layers 3, 4, and 7: Sophisticated DDoS events are detected and blocked without manual intervention, using AWS global threat intelligence.
- Application-specific traffic baselining: Normal traffic patterns are baselined per application so anomalies such as HTTP floods and DNS query floods are detected against actual behaviour.
- Packet filtering and traffic shaping: Deterministic packet filtering and priority-based traffic shaping are deployed inline to stop network-layer attacks.
- Shield Response Team access: Expert guidance is available from the Shield Response Team during active DDoS incidents, alongside customisable application-specific security controls.
- Protection for APIs and applications: SYN floods, UDP floods, and other reflection attacks are scrubbed at the relevant layers for applications and APIs.
- Network security director in preview: Network topology is visualised and prioritised by risk, with recommended services and rule sets for each configuration issue, and natural-language queries through Amazon Q Developer.
| Criterion |
Solution Fit |
Key Considerations |
| Mitigation capacity and scrubbing footprint |
Mitigation runs inline on AWS global infrastructure; the product page does not state a capacity figure. |
No published Tbps figure makes direct capacity comparison with scrubbing providers difficult. |
| Attack coverage across network and application layers |
Automatic mitigation across layers 3, 4, and 7, covering SYN floods, UDP floods, reflection attacks, HTTP floods, and DNS query floods. |
Reviewers report occasional false positives and note that attack notifications could carry more detail. |
| Time to mitigation and SLA commitments |
Always-on detection with automatic inline mitigation intended to minimise downtime and latency. |
The product page does not state a specific time-to-mitigate SLA. |
| Deployment model and infrastructure fit |
Native integration with AWS resources including CloudFront, Elastic Load Balancing, Route 53, and AWS WAF. |
Protection is scoped to AWS-hosted resources, so multi-cloud or external assets need a separate service. |
| Visibility, reporting, and incident support |
Shield Response Team support during incidents, plus topology visualisation and remediation recommendations in preview. |
Reviewers note that detailed diagnostics, proactive engagement, and cost protection are Advanced-tier only, and that billing can be confusing. |
8. Azure DDoS Protection
Best for: Azure virtual networks needing always-on network mitigation
Strengths: Adaptive tuning, 15-minute response SLA, Sentinel integration
Things to consider: Network Protection tier is costly and tuning options are set
Azure DDoS Protection applies always-on monitoring and automatic mitigation to resources on Azure virtual networks. Traffic is scrubbed at the network edge before it reaches applications, and protection covers all resources on a virtual network once enabled.
Mitigation uses adaptive tuning, which compares actual traffic against thresholds defined in a DDoS policy, and adaptive threat intelligence for more complex attacks. The service comes in two tiers, Network Protection and IP Protection, and is zone-resilient by default with no customer configuration required.
Key features include:
- Always-on monitoring with automatic mitigation: Network attacks are detected and mitigated automatically, with traffic scrubbed at the network edge before it reaches applications.
- Adaptive tuning against policy thresholds: Application traffic patterns are monitored for anomalies by comparing actual traffic against thresholds set in the DDoS policy.
- Multilayer coverage: A comprehensive set of layer 3 and layer 4 attacks is covered, along with common layer 7 attacks when combined with a web application firewall.
- Integration with the Microsoft security stack: The service works with Azure Monitor, Microsoft Defender for Cloud, Microsoft Sentinel, and the wider Microsoft security suite.
- Rapid response team with a 15-minute SLA: The DDoS Protection rapid response team assists with investigation, custom mitigation, and analysis within a 15-minute SLA.
- Cost protection: Costs from DDoS-related usage spikes such as app-scaling charges and bandwidth surges are reduced.
- Two service tiers: Network Protection and IP Protection cover different organisation sizes and cost requirements, with pricing that scales with cloud deployment and no upfront commitments.
| Criterion |
Solution Fit |
Key Considerations |
| Mitigation capacity and scrubbing footprint |
Traffic is scrubbed at the network edge across Azure regions; the product page does not state a capacity figure. |
No published capacity number, and coverage is tied to Azure region availability. |
| Attack coverage across network and application layers |
Layer 3 and layer 4 coverage natively, extending to common layer 7 attacks when paired with Azure Web Application Firewall. |
Layer 7 protection requires the separate WAF product on Application Gateway. |
| Time to mitigation and SLA commitments |
Always-on monitoring with automatic mitigation, and a 15-minute SLA for rapid response team engagement. |
The 15-minute commitment covers team response rather than time to mitigate. |
| Deployment model and infrastructure fit |
Enabled across all resources on an Azure virtual network, zone-resilient by default, with Network Protection and IP Protection tiers. |
Protection applies to Azure resources only, and reviewers note limited ability to tune how attacks are handled. |
| Visibility, reporting, and incident support |
Full attack visibility with actionable insights, plus telemetry, logging, and alerting through Azure Monitor and Sentinel. |
Reviewers consistently flag the cost of the Network Protection tier and ask for a more detailed interface. |
How DDoS Mitigation Providers Work
Traffic Filtering
Traffic filtering is a core technique used in DDoS mitigation services to distinguish between legitimate and malicious requests. Through predefined security rules and real-time analysis, filters examine incoming packets for anomalies such as suspect IP addresses, protocol violations, or known attack patterns. This allows only authorized traffic to pass through, blocking bots and malicious actors attempting large-scale denial attempts.
Effective filtering requires constant updates to signature lists and whitelists to adapt to new threats. Advanced filtering systems employ behavioral analytics and machine learning to identify suspicious traffic that traditional rule-based systems might miss. By employing these dynamic approaches, mitigation providers ensure that false positives are minimized while shielding the protected application from evolving threats.
Traffic Scrubbing
Traffic scrubbing diverts incoming network traffic through specialized data centers, or “scrubbing centers,” where malicious packets are removed and cleaned traffic is forwarded to the destination server. These scrubbing centers can process massive volumes of data, leveraging high-throughput hardware and sophisticated filtering algorithms to rapidly analyze and eliminate DDoS traffic at scale.
The scrubbing process involves not only dropping malicious requests but also reconstructing sessions or connections as needed to maintain service integrity for real users. Providers maintain geographically distributed scrubbing centers for responsiveness and redundancy, ensuring that latency is minimized and that even globally-distributed attacks can be neutralized before reaching the target infrastructure.
Automated Detection and Response
Automated detection and response systems are essential to the speed and accuracy of modern DDoS mitigation services. These systems use real-time analytics to monitor incoming traffic for sudden spikes, protocol anomalies, or abnormal request behaviors consistent with typical DDoS attacks. Upon detection, the system can automatically deploy countermeasures, such as activating filters or rate limiting, with minimal human intervention.
Scalability and flexibility are crucial for automated systems since the volume and sophistication of DDoS attacks are constantly increasing. Automated workflows are engineered to respond within seconds, adapting to changes in attack tactics as they occur. This rapid, adaptive response ensures that online services remain available to legitimate users, even during sustained or evolving attack campaigns.
Layered Defense
Layered defense, or defense in depth, is a practice where multiple security controls are deployed at different points across the network and application stack to protect against DDoS attacks. This approach combines various mitigation technologies like firewalls, intrusion prevention systems, and application-specific protections to address threats at every layer, from infrastructure to application.
By implementing layered defense, organizations reduce their reliance on any single point of failure and make it significantly more difficult for attackers to find and exploit vulnerabilities. This redundancy ensures that even if an attacker manages to bypass one layer, subsequent layers stand ready to detect and block malicious activities. This strategy increases the resilience of digital assets against increasingly complex and persistent DDoS attacks.
Conclusion
Choosing a mitigation service is about resilience, speed, and fit. Focus on complete attack coverage, fast and enforceable response times, and capacity that scales under stress. Ensure clean integration with your current architecture, keep latency low with well-placed inspection points, and demand precise detection with clear visibility and control. Round it out with strong, always-available support and a pricing model you can predict during peak events.